Digital Forensics Lab

Digital Forensics Laboratory

State-of-the-art forensic analysis facility for digital evidence examination, data recovery, and incident investigation.

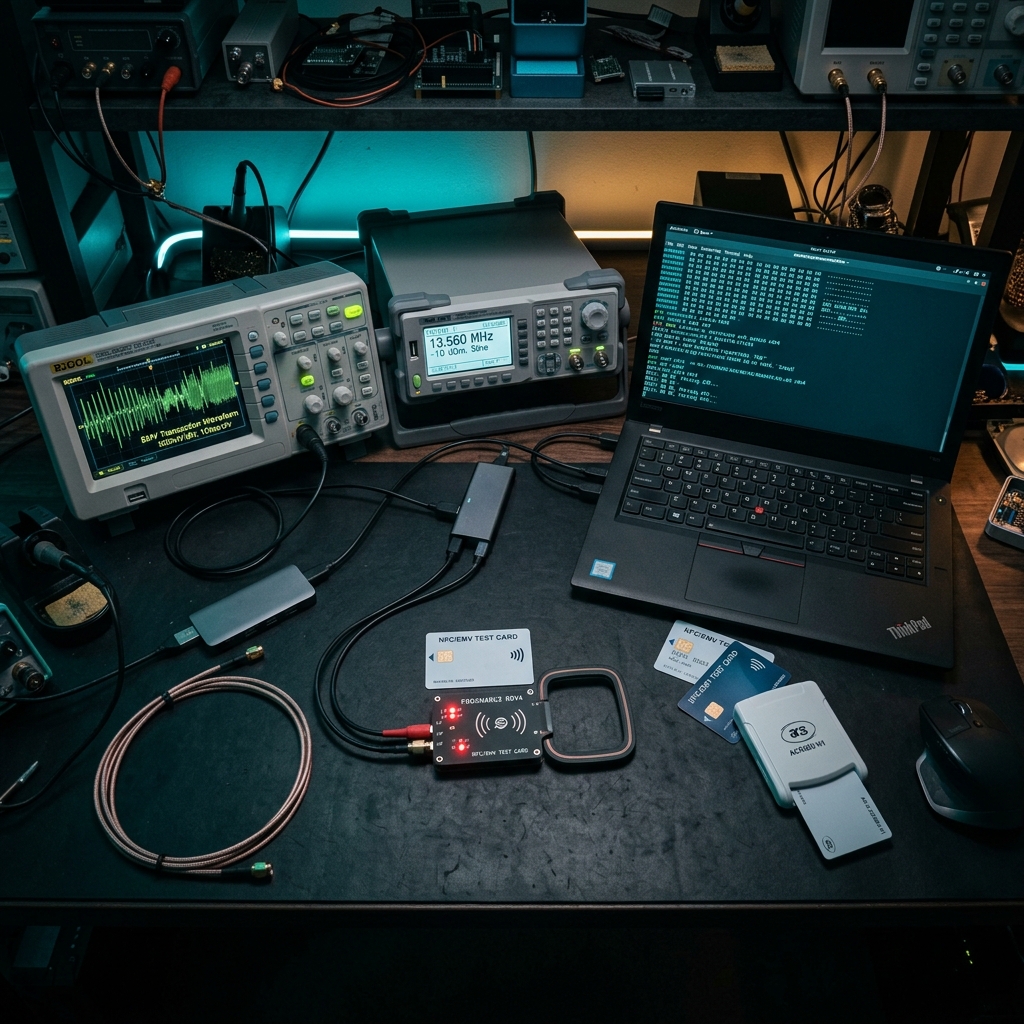
Digital forensics laboratory equipment

Our Laboratory

Our digital forensics laboratory is equipped with industry-leading tools and follows internationally recognized standards for evidence handling and analysis.

  • ✓ Evidence handling using ISO/IEC 27037 methodology
  • ✓ Faraday-shielded examination room
  • ✓ Hardware write-blockers for all media types
  • ✓ Licensed forensic software suite
  • ✓ Secure evidence storage facility
  • ✓ Chain-of-custody documentation

Forensic Services

Computer Forensics

  • ✓ RAM and volatile data capture
  • ✓ File system reconstruction
  • ✓ Deleted file recovery
  • ✓ Timeline analysis
  • ✓ Malware reverse engineering

Network Forensics

  • ✓ Network traffic capture and analysis
  • ✓ Intrusion detection and tracing
  • ✓ Log analysis and correlation
  • ✓ DNS and DHCP forensics
  • ✓ VPN and encrypted traffic analysis
  • ✓ Lateral movement reconstruction

Incident Response

  • ✓ 24/7 emergency response
  • ✓ Threat containment and eradication
  • ✓ Root cause analysis
  • ✓ Recovery and remediation planning
  • ✓ Post-incident reporting
  • ✓ Lessons learned documentation

Our Forensic Process

Every investigation follows a rigorous, documented methodology.

01

Intake

Case assessment, scope definition, and evidence intake with chain-of-custody initiation.

02

Preservation

Forensic imaging and evidence preservation using write-blocked, verified methods.

03

Analysis

Deep examination using industry-standard tools and custom analysis techniques.

04

Reporting

Comprehensive technical reports with documented findings and expert explanation support.

Need a Forensic Investigation?

Our team is available 24/7 for emergency incident response. Where relevant, evidence handling uses ISO/IEC 27037 as a methodology.

Engage +359 885 633 711